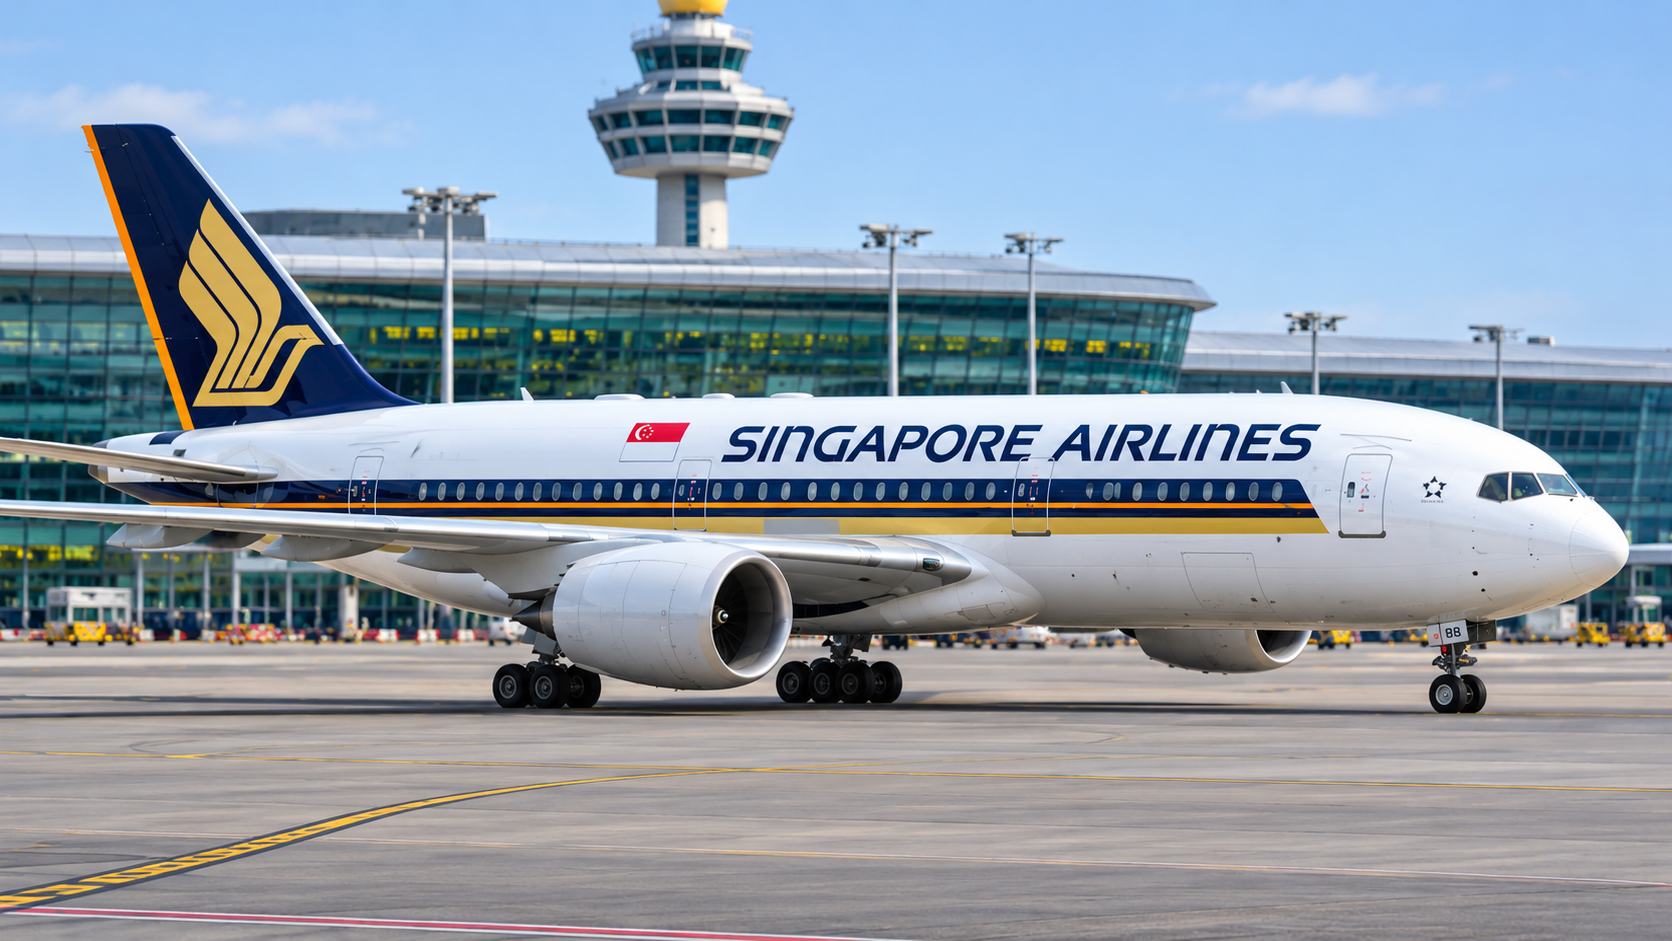
Singapore Airlines has disclosed that data relating to approximately 46,000 booking records was accessed without authorisation following a cybersecurity incident involving Amadeus, a third-party technology provider supporting airline reservation services.
In a statement issued on 3 November, the airline said the information accessed included customer names, booking reference numbers, travel itineraries and booking classes.
For approximately 620 booking records, additional personal information, including email addresses, telephone numbers, travel document details and KrisFlyer membership numbers, may also have been accessed.
Singapore Airlines said its own information technology systems had not been breached. According to the airline, Amadeus confirmed that bank account and credit card information had not been exposed and that no bookings had been modified.
As a precaution, the airline is contacting affected customers with upcoming travel plans to arrange changes to their booking reference numbers. Relevant authorities have also been notified.
Amadeus acknowledged a vulnerability affecting its travel booking display environment and said it had implemented corrective measures, alongside enhanced monitoring and detection capabilities.
Other airlines, including Malaysia Airlines, Cathay Pacific and Japan Airlines, have also disclosed incidents involving unauthorised access or potential exposure of reservation information associated with the technology provider.
The developments highlight cybersecurity risks within the interconnected systems supporting global airline reservations. Although Singapore Airlines reported no compromise of its internal systems, the incident demonstrates how vulnerabilities involving external service providers can affect passenger information across multiple carriers.
Amadeus said its investigation was continuing.
MyAviation Magazine | Aviation News Desk